DPDP Act 2023: What Every Gujarat Business Must Do Now
A practical guide to DPDP applicability, technical safeguards and readiness steps for MSMEs, manufacturers, healthcare organisations and businesses across Ahmedabad and Gujarat.
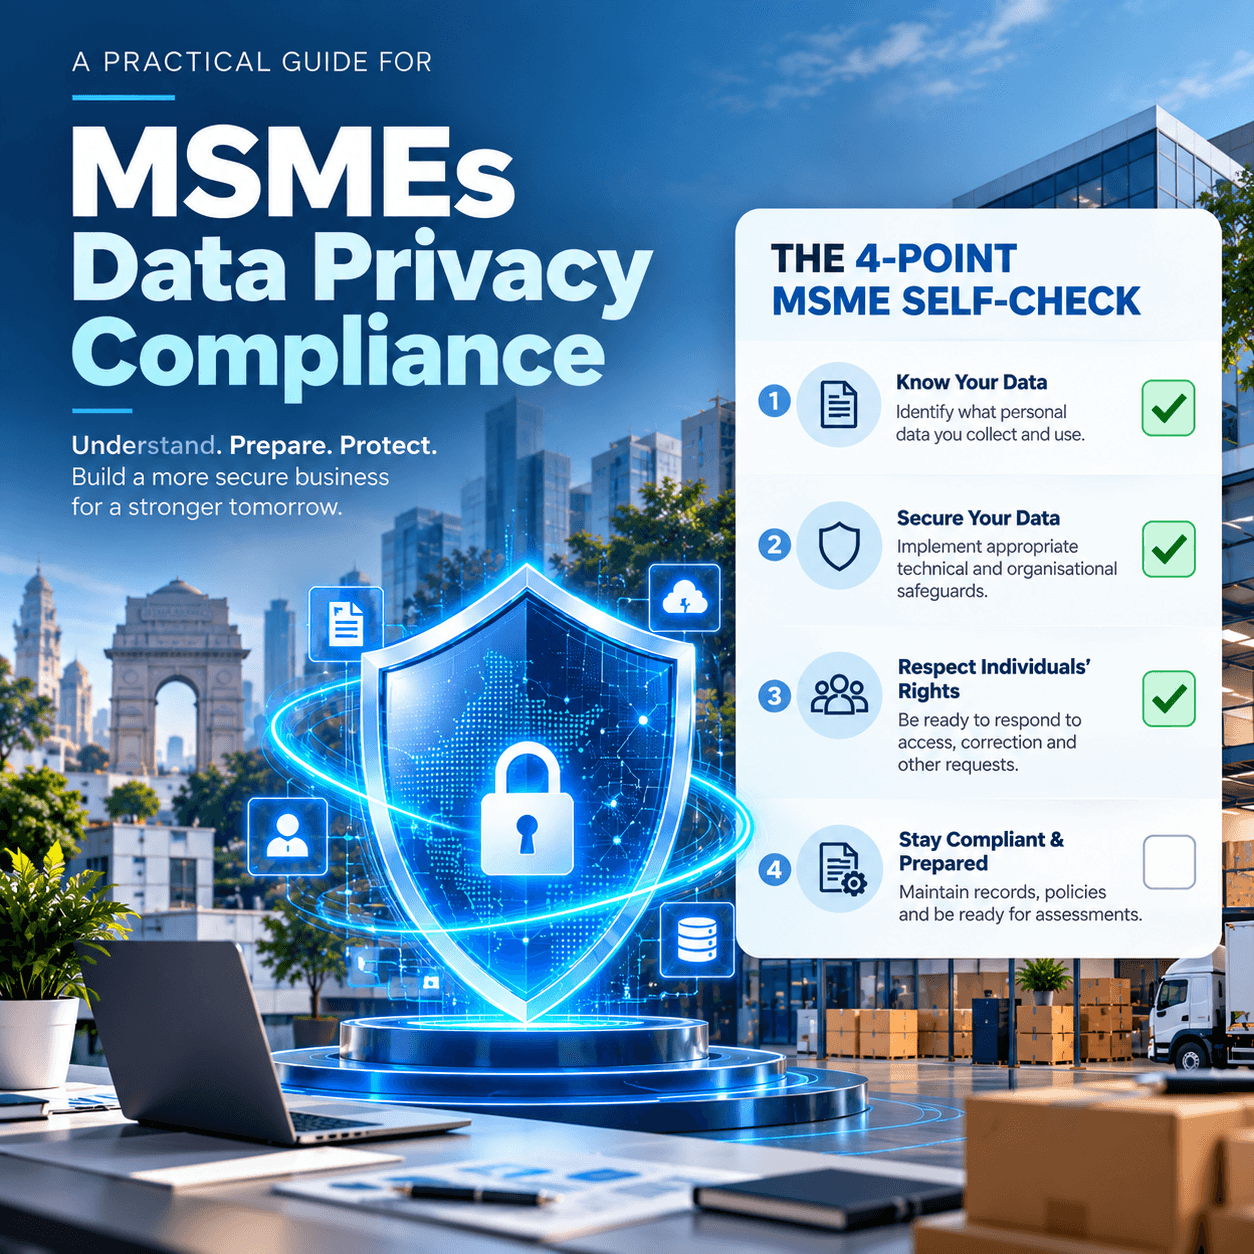
The Digital Personal Data Protection (DPDP) Act, 2023 establishes a framework for the processing of digital personal data in India. Gujarat businesses — including MSMEs, manufacturers, educational institutions, healthcare organisations and professional services companies — should evaluate how the Act applies to their activities and what technical, organisational and governance measures are required.
For organisations handling customer, employee, vendor or other personal data digitally, DPDP readiness can involve data discovery, access control, authentication, security monitoring, backup, encryption, incident response and appropriate documentation. However, the exact legal obligations and commencement dates should be assessed against the applicable provisions of the DPDP Act and Rules, and with qualified legal or privacy counsel where required.
What Is DPDP Compliance for a Gujarat Business?
DPDP compliance means establishing the legal, organisational and technical measures required for an organisation’s processing of digital personal data to comply with applicable requirements under India’s Digital Personal Data Protection framework.
For a Gujarat business, this may include:
- Identifying what personal data is being processed and where it is stored
- Reviewing access permissions across systems and teams
- Implementing appropriate authentication and security controls
- Protecting endpoints, servers and network infrastructure
- Maintaining appropriate backup and recovery controls
- Monitoring security events and maintaining audit logs
- Establishing documented incident-response procedures
- Reviewing third-party and processor relationships
- Maintaining appropriate documentation and evidence of controls
Technical controls are only one part of DPDP compliance. Legal, privacy, contractual and governance requirements may also apply — and should be addressed with appropriately qualified professionals.
DPDP Act Gujarat: Quick Answers
The DPDP framework can apply to organisations in Gujarat where their processing of digital personal data falls within the scope of the Act. Business size alone should not be treated as a blanket exemption — the Act does not specify minimum volume thresholds for standard Data Fiduciary obligations.
An organisation should first understand what personal data it processes, where that data is stored, who can access it, which systems process it, and what security controls are currently implemented. This data inventory and gap assessment forms the foundation of any DPDP readiness programme.
Depending on the organisation and its environment, relevant controls may include identity and access management, MFA, endpoint protection, firewall security, encryption, backup, logging, monitoring, vulnerability management and incident response. The appropriate controls depend on the nature and volume of data processed.
No. Technical security is one component of a broader DPDP compliance programme. Privacy, legal, governance, contractual and organisational requirements also need to be addressed — including consent processes, data principal rights, breach notification, and appropriate vendor agreements.
An IT infrastructure or cybersecurity provider can assess and document technical controls within its scope — covering infrastructure, security tools, access controls, backups and logging. Legal interpretation and other specialised compliance requirements may require appropriately qualified privacy or legal professionals.
What Is the DPDP Act 2023?
The Digital Personal Data Protection Act, 2023 is India’s statutory framework governing the processing of digital personal data. It received Presidential assent on 11 August 2023. The Digital Personal Data Protection Rules, 2025 were subsequently notified by the Ministry of Electronics and Information Technology (MeitY) on 13 November 2025, with phased commencement dates specified therein.
Presidential assent received. Read the official Act — MeitY PDF
MeitY notified the DPDP Rules, 2025. Phased commencement framework established. Read the Rules — MeitY PDF
Rule 4 relating to Consent Manager registration is scheduled to come into force. Organisations collecting personal data through digital channels should review their consent processes before this date.
Notice, consent, Data Fiduciary duties, Data Principal rights and breach reporting obligations are scheduled for commencement 18 months after the Rules. Organisations should use this period to implement required controls rather than wait.
Source: MeitY DPDP Act & Policies Repository
Does the DPDP Act Apply to Gujarat Businesses?
The DPDP Act applies to the processing of digital personal data in India where data is collected digitally, or collected in non-digital form and subsequently digitised. It also applies to processing outside India in connection with offering goods or services to Data Principals in India.
Organisations across Gujarat — manufacturers in GIDC industrial estates, textile exporters in Surat, pharmaceutical companies in Vadodara, financial entities at GIFT City, hospitals and diagnostic centres in Ahmedabad, educational institutions, logistics and professional services companies — may fall within scope if they process digital personal data of individuals.
Business size alone should not be treated as a blanket exemption. However, specific applicability, any applicable exemptions, and the precise obligations that apply should be assessed based on the nature of an organisation’s processing activities and with appropriately qualified legal or privacy advice.
What Personal Data Should a Business Identify?
A foundational step in any DPDP readiness programme is identifying what personal data the organisation processes and where it resides. For most Gujarat businesses, this includes:
- Customer and lead data — names, phone numbers, email addresses, billing and delivery addresses, WhatsApp enquiries
- Employee and candidate data — resumes, Aadhaar and PAN scans, salary records, biometric attendance, appointment letters
- Vendor and B2B partner data — personal contact details held in CRM, ERP or email
- Website and app data — form submissions, cookies, analytics data
- Digitised records — paper files, visitor logs or historical records once scanned or keyed into digital systems
The inventory should map where each category of data is stored, who has access, how long it is retained, and whether third parties process it on the organisation’s behalf.
What Technical Safeguards Should Businesses Review?
The DPDP Act requires Data Fiduciaries to implement reasonable security safeguards to prevent personal data breaches. While the Act does not prescribe specific technologies, the following controls are commonly relevant for Gujarat businesses reviewing their technical posture:
Identity and Access Management
Role-based access controls on shared drives, NAS, ERP and Tally/HRMS systems — ensuring employees can only access data relevant to their role. Multi-factor authentication (MFA) on admin and business email accounts adds a critical layer of protection against unauthorised access.
Endpoint and Gateway Security
A hardware firewall or UTM appliance at the office gateway, combined with centralised endpoint protection (EDR), provides perimeter and device-level security. For context, common hardware platforms used in Gujarat business environments include Sophos XGS and FortiGate series appliances, sized by user count and branch requirements.
Encryption
Full-disk encryption (BitLocker on Windows, FileVault on Mac) on all employee laptops and workstations. Encrypted storage for sensitive data at rest, and encrypted transmission for data in transit.
Backup and Recovery
A structured backup approach — typically three copies of data across two media types with one offsite or immutable copy — protects against ransomware, accidental deletion and hardware failure. Quarterly restore tests verify that backups are actually recoverable.
Logging and Monitoring
Centralised audit logging from ERP, cloud drives, switches and core servers — retained for an appropriate period — provides the forensic record needed to investigate a suspected breach. Without logs, it can be difficult to determine the scope of an incident.
Vulnerability and Patch Management
Regular OS and application patching across all devices, combined with periodic vulnerability assessments, reduces the attack surface available to malicious actors.
Incident Response
A documented incident-response procedure — including how to detect, contain, assess and report a suspected breach — enables a coordinated response rather than an ad hoc one. Under DPDP, breach notification obligations may apply once the relevant provisions are in force.
Need to Assess Your IT Environment?
A DPDP readiness programme should include more than policy documentation. Review your existing IT infrastructure, security controls and technical evidence to identify gaps and prioritise remediation.
Serving Ahmedabad, Surat, Vadodara, Rajkot, Gandhinagar and all of Gujarat.
What Evidence Should a Business Maintain?
Technical controls alone are not sufficient — organisations should also maintain documented evidence that those controls are in place and functioning. This is particularly relevant for organisations that may need to demonstrate their security posture during regulatory enquiries or audits. Evidence to maintain includes:
- Access-control records and user permission lists
- MFA configuration screenshots or reports
- Endpoint security deployment and status reports
- Firewall configuration and rule documentation
- Backup job reports and restore-test records
- Vulnerability assessment and patch management reports
- Security event logs (retained for an appropriate period)
- Incident-response documentation (even for incidents that did not result in a breach)
- Data inventory and processing records
- Vendor and processor agreements relevant to personal data
DPDP Compliance Checklist for Gujarat MSMEs
- Completed a data inventory — know what personal data you hold and where
- Mapped data flows across systems, departments and third-party processors
- Reviewed and restricted user access permissions by role
- Enabled MFA on all admin and business email accounts
- Deployed centralised endpoint protection (EDR) across all devices
- Installed and configured a hardware firewall or UTM at the office gateway
- Implemented encrypted backup with a tested restore process
- Enabled full-disk encryption on employee laptops
- Set up centralised audit logging with appropriate retention
- Documented an incident-response procedure
- Reviewed SaaS and cloud platform vendor agreements for data processing provisions
- Added a privacy notice to the company website
- Established a grievance/privacy contact within the organisation
- Engaged legal or privacy counsel to assess specific DPDP obligations
Common DPDP Compliance Mistakes to Avoid
- No data inventory — not knowing what personal data you hold or where it is stored
- Excessive user permissions — staff can access data unrelated to their role
- No MFA — admin and email accounts protected only by passwords
- Poor or untested backup practices — backups exist but restores have never been verified
- No documented incident-response procedure — no plan in place when an incident occurs
- Uncontrolled SaaS accounts — personal data flows into unreviewed third-party platforms
- No evidence of security controls — controls exist but are not documented or auditable
- Assuming antivirus alone provides adequate endpoint protection
- Treating DPDP as only a legal task — ignoring the technical safeguard requirements
- Waiting for a final commencement date before starting implementation
How to Start a DPDP Technical Readiness Assessment
A structured DPDP technical readiness assessment typically involves the following steps:
- Data and system inventory — identifying what personal data is processed and which systems are involved
- Access control review — assessing who has access to personal data and whether permissions are appropriate
- Security control gap analysis — reviewing current controls against DPDP’s reasonable safeguard requirements
- Evidence review — checking what documentation and logs currently exist
- Remediation roadmap — prioritising actions by risk and effort
- Implementation — deploying the required controls and documenting them
- Evidence pack — assembling documented proof of each control for future reference
Kirti Telnet Pvt. Ltd. provides DPDP Technical Compliance Assessment and Implementation services for Gujarat businesses — covering the infrastructure, security controls and evidence documentation layer. Legal and governance requirements should be addressed with qualified privacy and legal professionals.
For organisations that may qualify as Significant Data Fiduciaries, additional obligations apply including independent data audits and Data Protection Impact Assessments — for which an IT partner can prepare the technical environment and evidence, while legal assessment is conducted separately.

No comment